
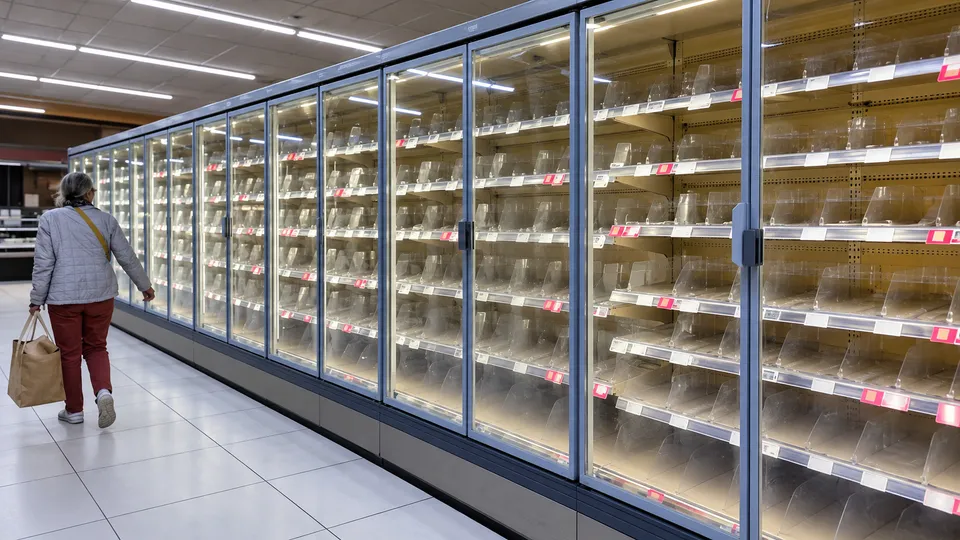
One Sunday night this month, the cold went out of French supermarkets. Nobody forced a door or cut a cable. According to CNN, attackers took over the refrigeration controls from a distance and switched the display cases into defrost mode. Some units were driven up to 50C. Food spoiled, and in some stores electrical fires broke out. Roland Lescure, the finance minister, put the toll at about 700 of the country’s 10,000 supermarkets. The first night of the attack is told in an earlier rews story.
It is an old pattern. When a great system breaks, the cause usually turns out to be small: a habit nobody questioned, a box nobody owned, a budget line nobody wanted to sign.
A password written by the calendar
Dan Goodin, writing for Ars Technica, traces the damage to neglect rather than genius. The affected stores were running controllers on outdated firmware. They also likely failed to hide the devices behind a VPN and to keep a restricted list of IP addresses allowed to log in. Both precautions are standard practice, and both are often skipped.
Researchers at the British security firm Pen Test Partners have described how the break-in worked, in a post published on 14 October. The machines at the centre of it were Danfoss AK-SM and AK-SC system managers, the units that set the temperature for every case in a store. Many were connected through a contractor’s cellular modem, “on a link the retailer often does not own, cannot see, and has no record of.” To get to 50C, the attackers kept the defrost heaters running. The system manager let them push that setting to every case controller at once and silence the alarms that should have gone off.
The way in was almost mocking. On older units, a hidden login path handed out an administrative session to anyone who supplied the right code. That code, the researchers write, “is generated from the device’s date by a fixed algorithm, with no per-device secret,” so that “the same code is valid on every unit for a given day.” The flaw is catalogued as CVE-2025-41450, and Danfoss removed the path from release 4.2 onwards. A store that never upgraded kept a lock whose key was the date on the calendar.
Discontinued, end-of-life
Danfoss was not the only maker involved. France’s cybersecurity agency, ANSSI, told CNN that the hackers got into controllers from at least three companies: Danfoss of Denmark, Copeland of the United States, and Dixell, which Copeland owns.
The manufacturers answered in the language manufacturers use. Copeland told Ars Technica by email that it had found a vulnerability “identified in a discontinued, end-of-life generation of controllers” and was working with customers to prevent anything similar. Danfoss did not immediately answer Ars Technica’s questions. CNN reported that Danfoss also pointed to discontinued models, saying many of the affected units “no longer receive software or security updates” or were “running outdated software.”
Read one way, that is an explanation. Read another, it is a description of the stock in hundreds of stores: equipment the people who made it had stopped looking after, still holding the milk and the meat.
Nobody can say they weren’t warned. The security firm Claroty flagged the danger of ignoring these basic steps last October, and the US Cybersecurity and Infrastructure Security Agency issued its own warning in February. Pen Test Partners now lists the steps that would have kept the attackers out:
Cyber hygiene would have prevented the access: take the controller off the public internet, put remote access behind a VPN and an IP allowlist, bring third-party kit onto the network in a controlled, owned and documented way rather than leaving it on a contractor’s own connection, change known and default credentials, and patch to a current release.
Silence, and the bill
France was not the only country hit. Ars Technica reports that stores in Spain, Portugal, Poland, Germany and Belgium were also affected, and estimates that the mass hack likely cost tens or hundreds of millions of euros.
Nobody has claimed it. No one has demanded a ransom or bragged online. That silence leaves two possibilities, Ars Technica suggests: vandalism on a mass scale, or a nation-state or other foreign actor trying to disrupt a whole continent. Pen Test Partners, as the title of its post makes clear, thinks a state is not needed to explain it. The firm adds a warning of its own. In separate research still going through coordinated disclosure, it found internet-exposed controllers from another vendor that a botnet had already compromised. “Someone is collecting footholds on the same class of device,” the researchers write.
The ledger
Behind the warm cases sits an older contest inside most companies, between the people who guard the money and the people who guard the systems. A new controller costs real money and earns nothing back on the day it goes in, while the old one still keeps things cold. So the old one stays. Its contractor’s modem keeps blinking in a back room, connected to the whole world and recorded on nobody’s inventory.
One could put it like this: for an institution, a risk becomes real only once it has a price. Until then it belongs to the engineers. Afterwards it belongs to the board.
Executives at the supermarket chains that were hit will probably learn that lesson now, at a cost of spoiled stock and burned wiring. Whether chains that were spared will spend the money before their own Sunday night is much less certain. Pen Test Partners, meanwhile, says someone is already collecting footholds on the next batch of devices.