
The television box is a humble citizen of the modern home. It sits beneath the screen, it costs about fifty-five dollars, it exists to stream films and idle through the night. Researchers at Anthropic bought fifteen of them — off-brand, no pedigree, four gigabytes of memory apiece — and asked them, together, to think.
Linked in a cluster, each box holding only a shard of the whole, the fifteen ran Google’s open-weight model Gemma4-26B-A4B, 26 billion parameters, with no data centre and no specialised processor. They produced 0.39 tokens per second — words far more slowly than any chatbot speaks, but words all the same. The experiment, led by William Zhou and Daniel Freeman and published on 12 October, as TechTimes reported, posed a question that belongs equally to crime and to war: could a small artificial mind cross from device to device the way a worm crosses a network?
The company’s answer, from its Frontier Red Team, is: not yet, but soon. Where the old internet-of-things worms — Mirai and its descendants — planted the same crude payload everywhere, an AI worm could read each target it met and write its exploit to fit. Anthropic calls the hypothetical creatures small weight-based replicators.
A worm that leaves notes
The company’s agents, equipped with common exploitation tools such as reverse shells, followed a four-beat rhythm: find targets, gain code execution, establish inference, propagate to new hosts. What distinguishes them from the dumb worms of old, as Dan Goodin described in Ars Technica, is that they learn on the job: a replicator that fails against one device leaves behind a list of prompts, code and notes, so its descendants do not waste themselves repeating its mistakes. The parasite keeps a diary.
Such an ‘AI worm’ could carry its model weights with it as it reproduces (or re-download them from a public hub), and then run inference directly on compromised hardware. Effectively, the weights would become part of the malware payload.
The hardest stage, Anthropic found, is persuading unfamiliar hardware to run a model at all — choosing compatible inference software, installing dependencies, debugging platform-specific bugs. “These steps are serially dependent, and failures are difficult to recover from,” the company said. At 0.39 tokens per second the labour is also glacial: a full inference setup for the unoptimized Gemma model would take 71 to 150 hours, and 29 to 51 hours for the smaller Qwen3.5-9B.
What the laboratory actually showed
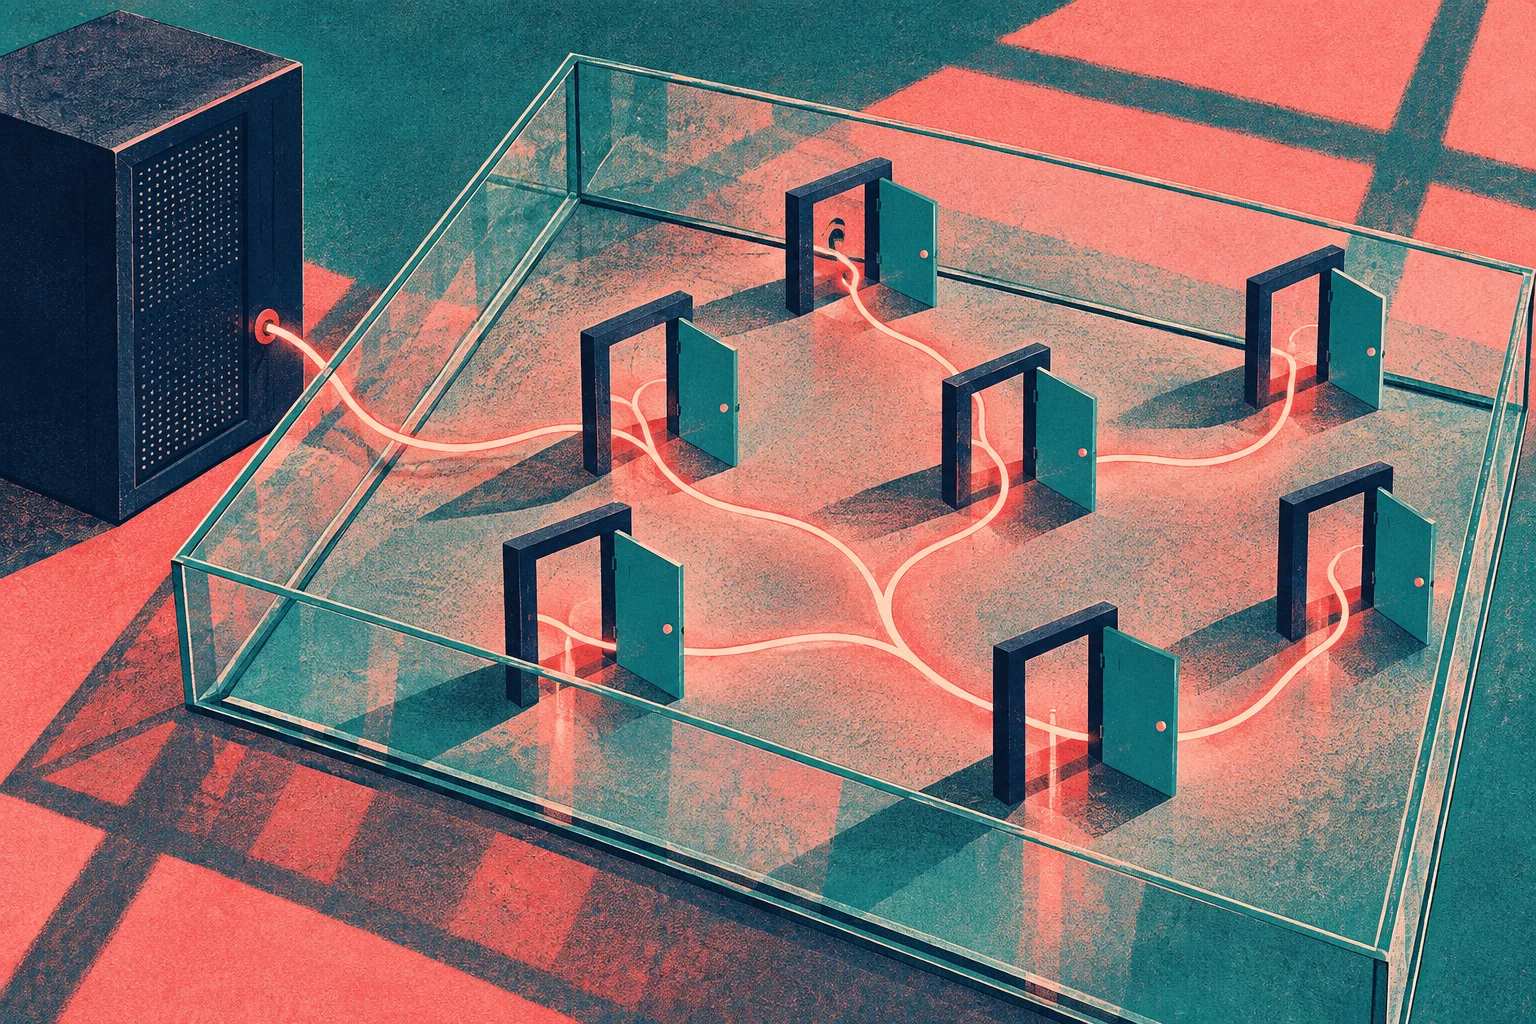
The fullest demonstration belonged to GLM-5.2, an open-weight model from the Chinese developer Z.ai. Inside a firewalled network of eight Google Cloud nodes running Android emulators, it orchestrated a simplified replication that reached all eight nodes in four of five trials and seven in the fifth. But the doors had been left conspicuously unlocked — the simulated devices exposed an unauthenticated Android Debug Bridge port, and Anthropic itself calls the result an upper bound on real-world success. GLM-5.2, moreover, never ran on those machines; it operated through a separate inference server while the conquered nodes were configured to run the smaller Llama3.1-8B. No one built a self-contained worm, and no smart television was harmed.
Between what is small enough and what is capable enough there remains a gap. Models under roughly 30 billion parameters can perform individual steps of replication but fumble the full chain; GLM-5.2 is too large to live on cheap hardware. Anthropic’s projection — that small models could match this capability by the end of 2026 — rests on historical improvement rates used only as a proxy, and the researchers say so. The company blog called the prospect a “digital slime mold,” as Gizmodo’s Webb Wright noted, adding that earlier this year a team of academics had already used an anonymous open-source LLM to build an AI-powered worm spreading across Linux, Windows and IoT devices by exploiting common flaws like reused passwords.
The arithmetic of the infected
For scale, Anthropic looked to Kimwolf, a conventional IoT botnet reportedly holding more than two million devices, most of them cheap Android TV boxes. If fifteen devices are needed to run each 26-billion-parameter model, Techstrong.ai calculated from the company’s figures, a network that size could host roughly 133,000 model instances — and all of them together would equal no more than about 40 NVIDIA H100 GPUs. Slow work, each replication cycle needing more than a day or two. But a headless thing spread across millions of kitchens does not die when part of it is cut away.
The candidate hosts are already in the house. “Machines that could run a significant model shard for a <30B model include smart fridges, smart ovens, automatic vacuum cleaners, and lawnmowers,” Anthropic wrote, as Yahoo Finance reported — and newer devices ship with built-in AI chips, which the company says will make them more attractive still. The warning lands as Apple debuts its HomeView and after a report that hackers broke into internet-connected refrigerators in French grocery stores, raising temperatures, ruining food and starting fires. The appliances, it turns out, are already contested ground.
The skeptics at the gate
Not everyone in the security world is frightened. Ciaran Martin, former head of Britain’s National Cyber Security Centre, told Reuters the work is technically interesting but carries an element of vendor exaggeration. Marco Figueroa, who leads Mozilla’s bug bounty program, was blunter: “AI safety deserves rigorous science, not fear mongering driven marketing dressed up as a breakthrough.” Others leaned the other way — Zhengxiong Li of the University of Colorado Denver told Reuters that an AI running across many devices without a central service could prove very hard to shut down — while Jessica Ji of Georgetown’s Center for Security and Emerging Technology cautioned that autonomous proliferation is possible but far from inevitable.
“Anthropic tested the hard part honestly,” Justin Beals, CEO of the compliance platform Strike Graph, told Techstrong. “Today, a slow worm on cheap hardware is a real but modest threat.” His prescription has the flavour of preparing for weather one has been told is coming: “Inventory every device, kill default credentials, and watch for sustained traffic between devices that have no business talking to each other. Manufacturers should be held to secure defaults now, before the models get there.”
There is a familiar irony in a frontier lab racing to build minds while warning investors that AI could pose an existential risk — and now warning householders about the worms those minds may inspire. The ruled, meanwhile, are offered the usual instruments: since 29 April 2024 Britain has required makers of connected products to ship with unique passwords, publish channels for reporting vulnerabilities and disclose how long security updates will last. “We should aim to harden our systems to make it difficult for such replicators to spread,” Anthropic writes, “but also prepare to deal with a world where they are here to stay.”